MOVEit Transfer App's Third Bug Found During Mass Cl0p Ransomware Attack
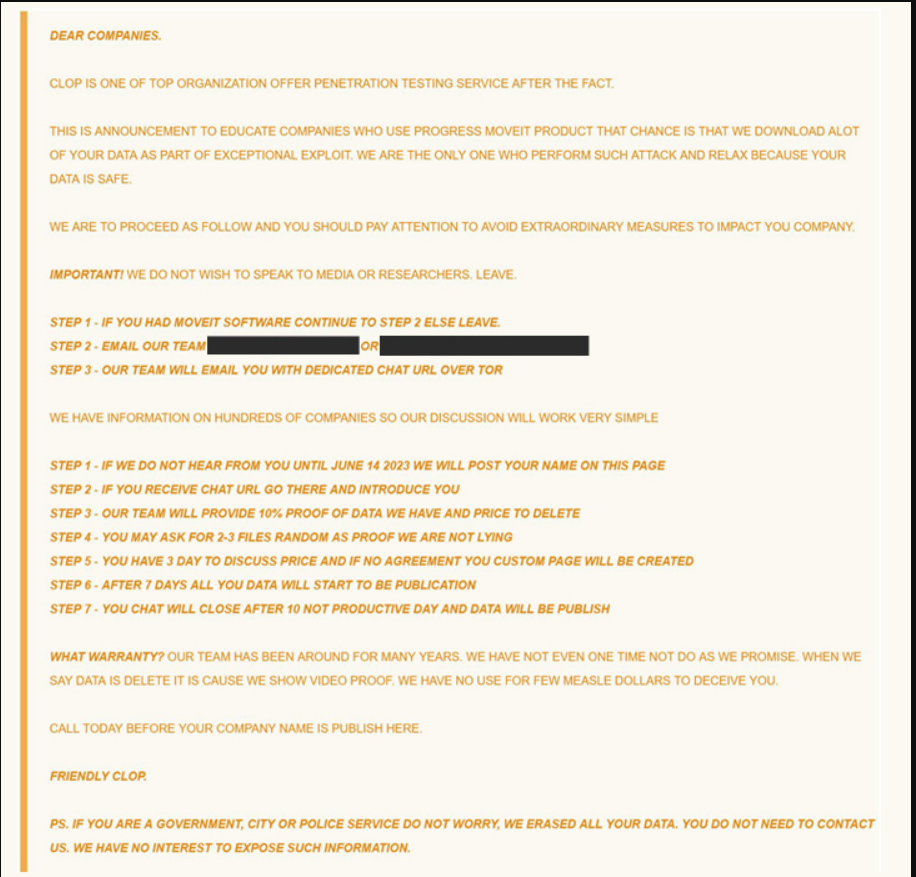
Progress Software recently disclosed a number of serious vulnerabilities affecting their MOVEit Transfer tool. The business issued a warning that these flaws might result in data breaches, unauthorised access to the environment, and privilege escalations. The disclosure follows extortion strategies used by the Cl0p cybercrime organisation, which targeted businesses afflicted by the flaws. The specifics of the vulnerabilities, their possible effects on impacted organisations, and the broader ramifications for cybersecurity will all be covered in this article. Overview of MOVEit Transfer Vulnerabilities: Three flaws were found in the MOVEit Transfer programme by Progress Software. Two of these flaws were connected to SQL injection attacks, but the third has not yet been given a CVE number. The SQL injection flaws can be used to access the application's database without authorization. A similar risk of privilege escalation and unauthorised access to the environment is also present due...